API security basics every developer should know

APIs power mobile apps, websites and partner integrations, which also makes them a favorite target. Many API breaches come not from clever hacking but from basic gaps in who is allowed to do what.
Authenticate and authorize every request
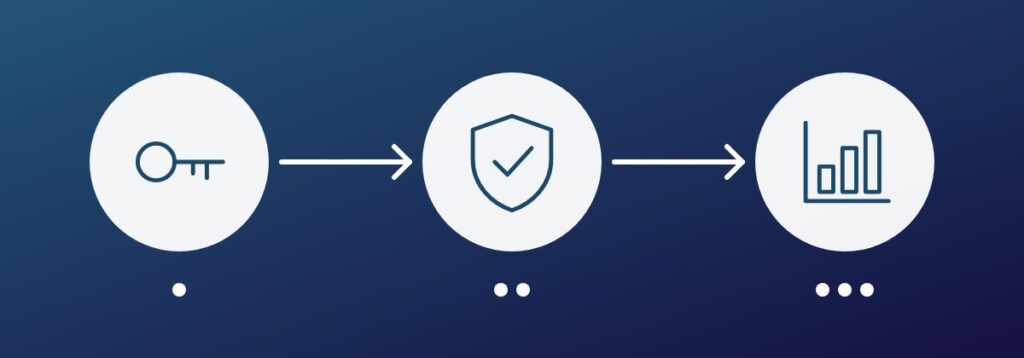
Authentication proves who is calling. Authorization decides what that caller may touch. A frequent flaw is checking the first but not the second, so one user can read another user’s records by changing an ID in the request. Check ownership on the server for every object.
Validate everything and limit the damage
Treat all input as untrusted. Validate type, length and format, and reject what you do not expect. Add rate limits and sensible timeouts so a single client cannot overwhelm the service or guess credentials endlessly.
- Use short-lived access tokens and rotate keys regularly
- Return only the fields the client needs, never whole database rows
- Send errors that help developers without revealing internals
- Log access attempts without storing passwords or tokens
Manage versions and test
Keep an inventory of every endpoint, including old versions, and retire them on a published schedule. Test regularly with tools that probe for broken access control and excessive data exposure.
Key takeaway: assume every request is hostile until the server has verified who sent it and what they may do.